
AI Governance · Privacy · Security
Govern, secure and prove every AI decision – inside your perimeter.
Fidempli combines an AI governance platform with consulting, professional and managed security services. We help you meet the EU AI Act and GDPR, protect personal data in every prompt, and keep evidence your auditor can trust – at any scale.
Hamburg-based · English & German · 12+ years in security and privacy
- Built for European requirements
- EU AI Act
- GDPR
- NIS2
- DORA
- ISO/IEC 42001
- ISO/IEC 27001
- NIST AI RMF
- in security and privacy
- 12+ years
- headquarters
- Hamburg
- delivered in English and German
- EN · DE
- platform launch
- December 2026
The challenge
AI is already inside your organisation. Your controls are not.
Shadow AI and agents everywhere
Copilots, agents and personal AI accounts move customer and employee data today, often with no named owner.
European rules on several clocks
The EU AI Act, GDPR, NIS2 and DORA each ask for different proof, on different timelines.
Policies that are never enforced
Rules in PDFs and approvals in spreadsheets do not stop a prompt and do not convince an auditor.
The platform
See every capability with example data.
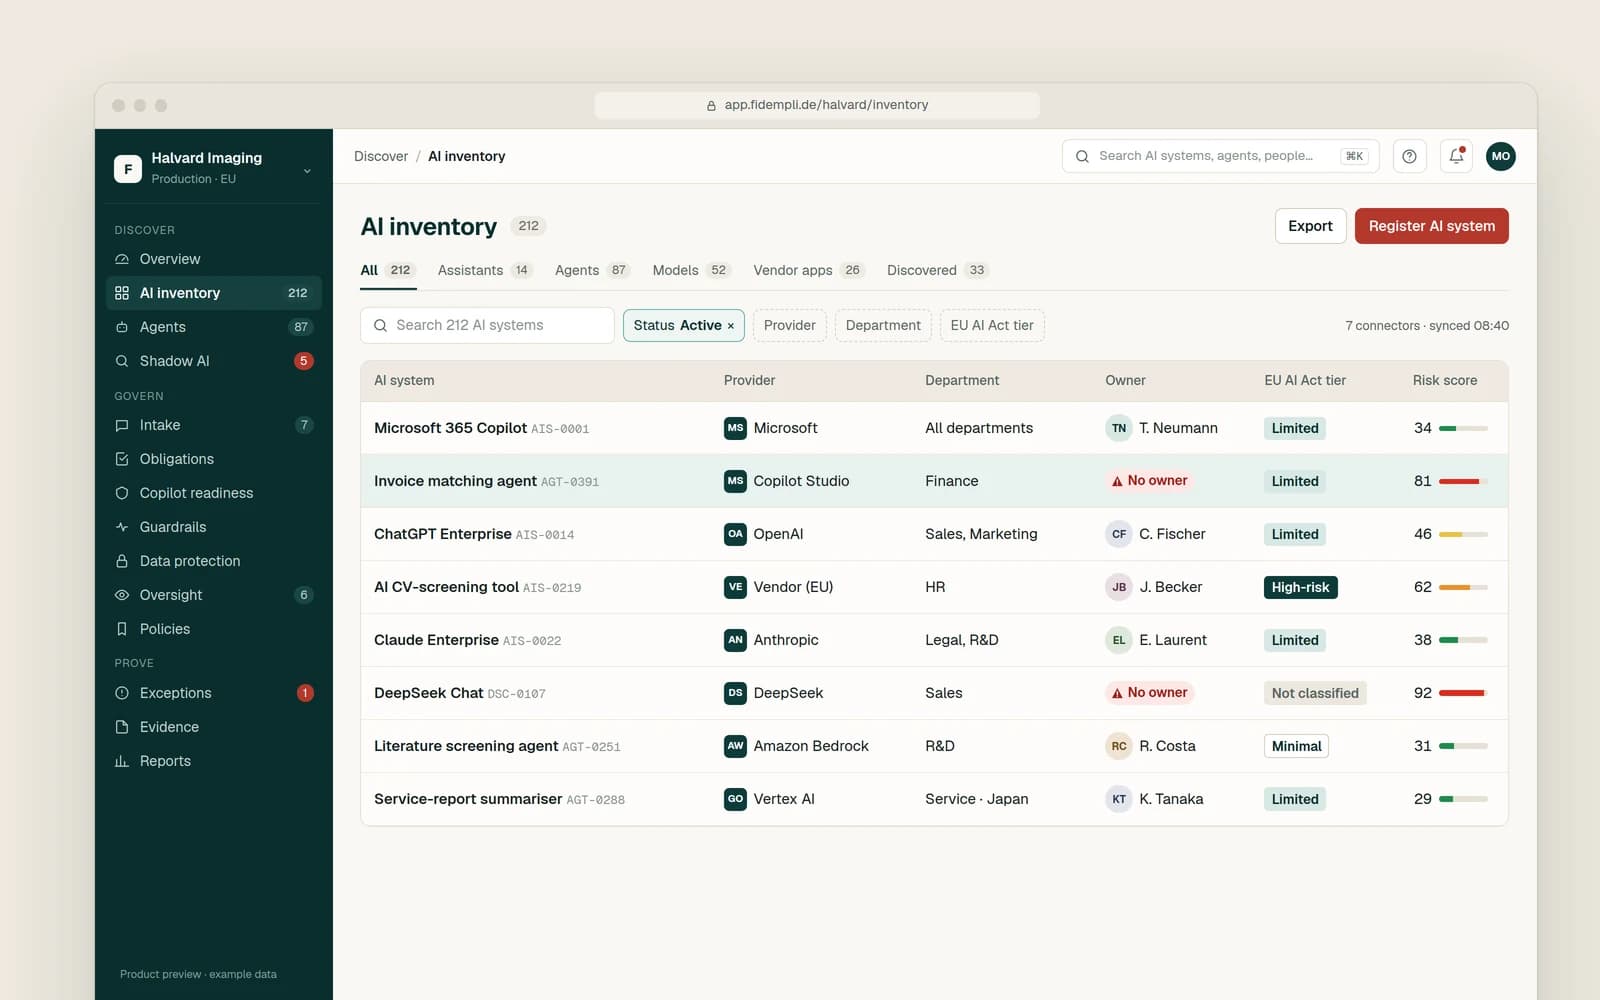
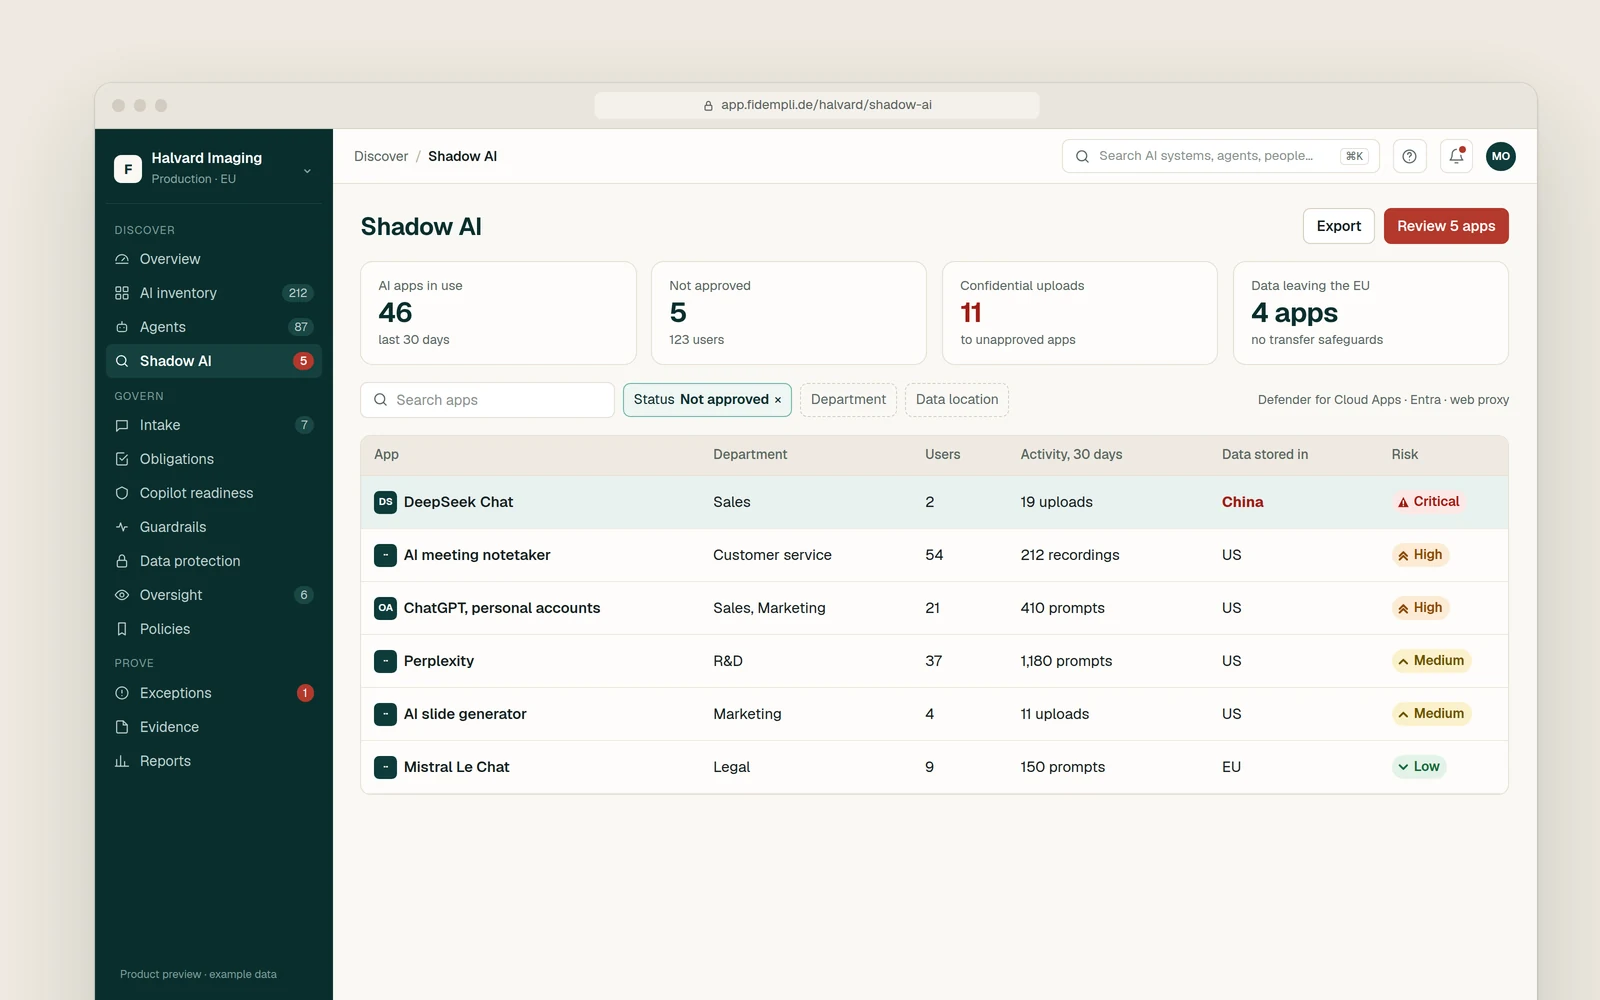
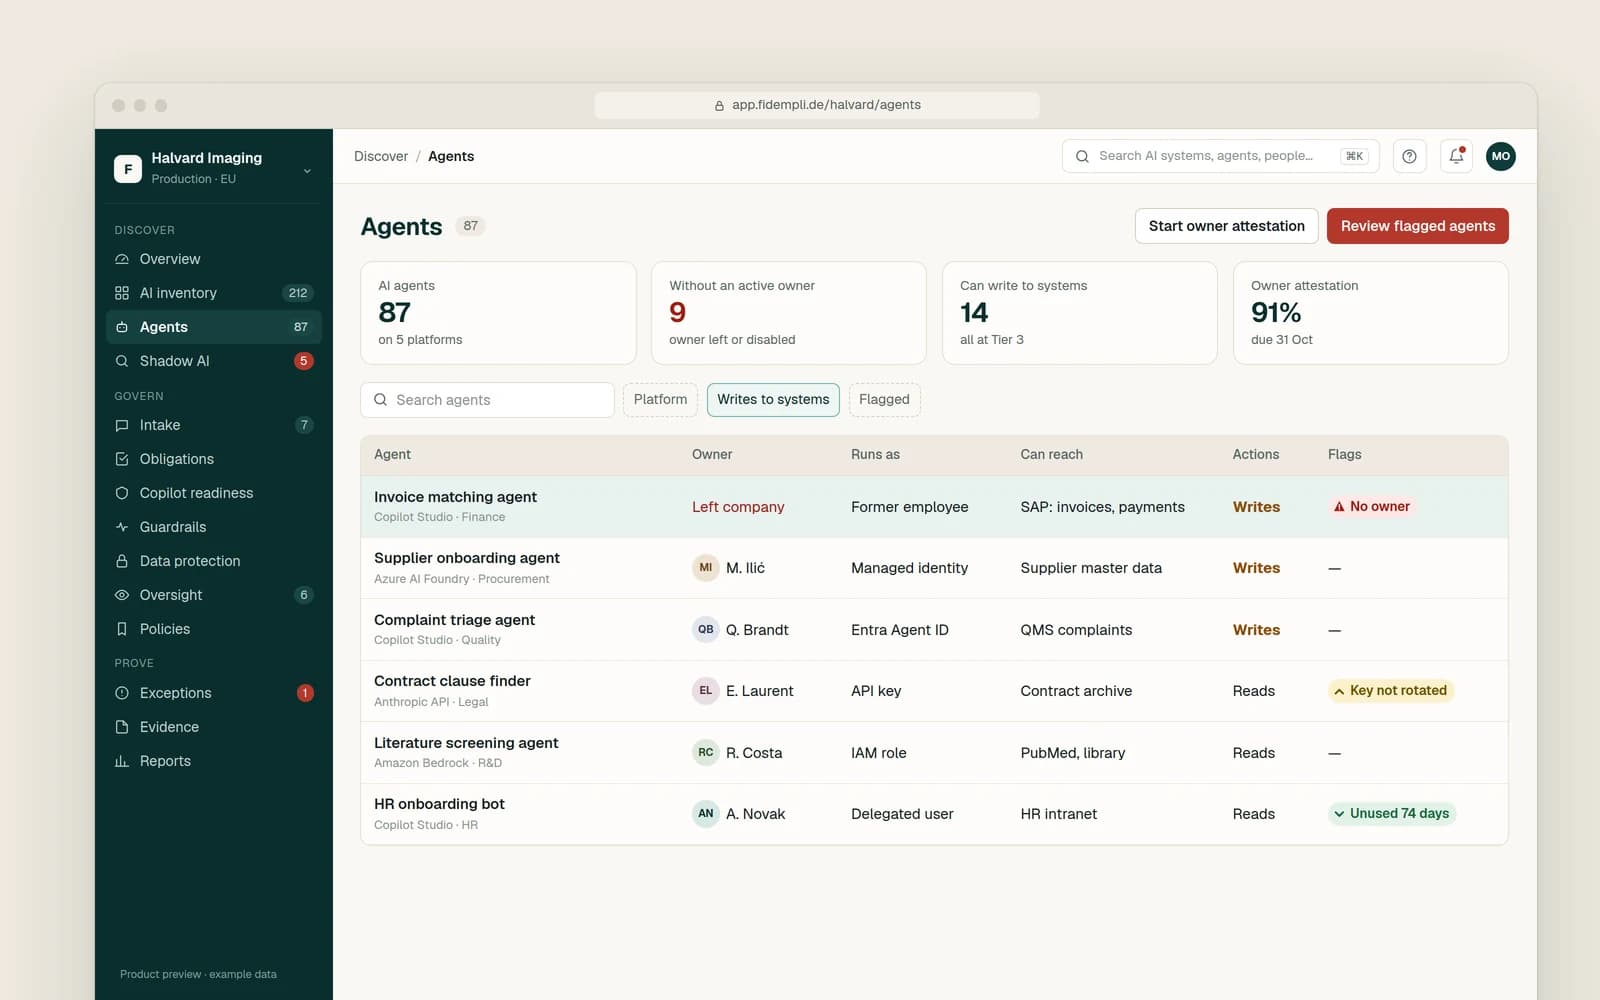
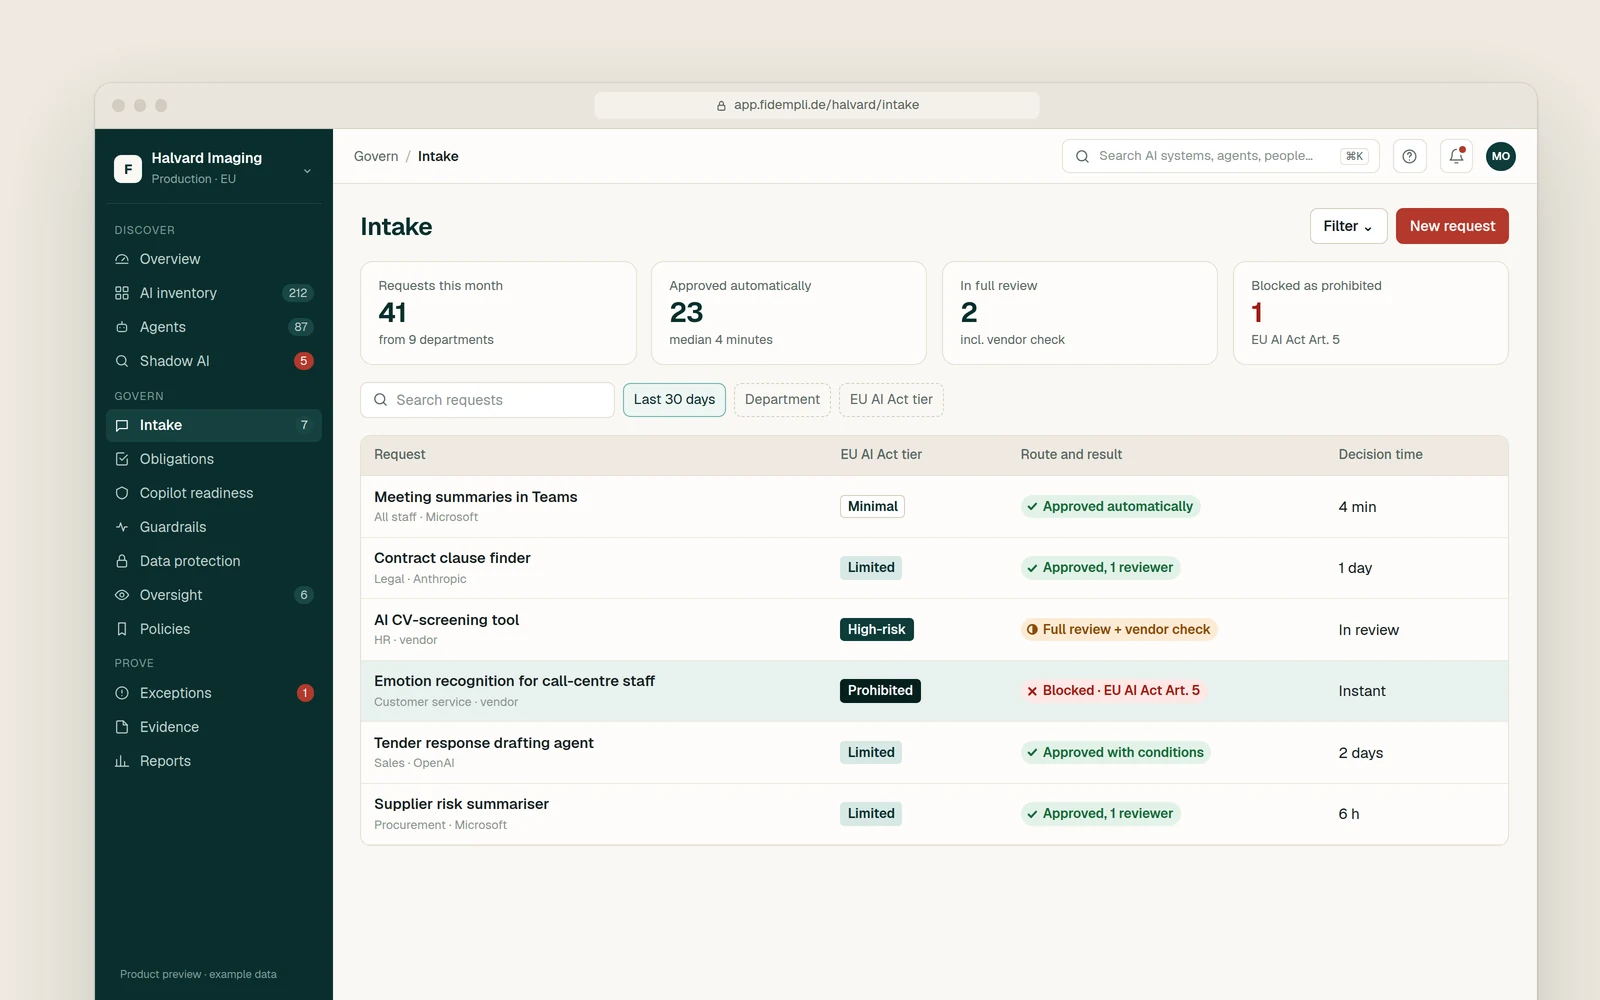
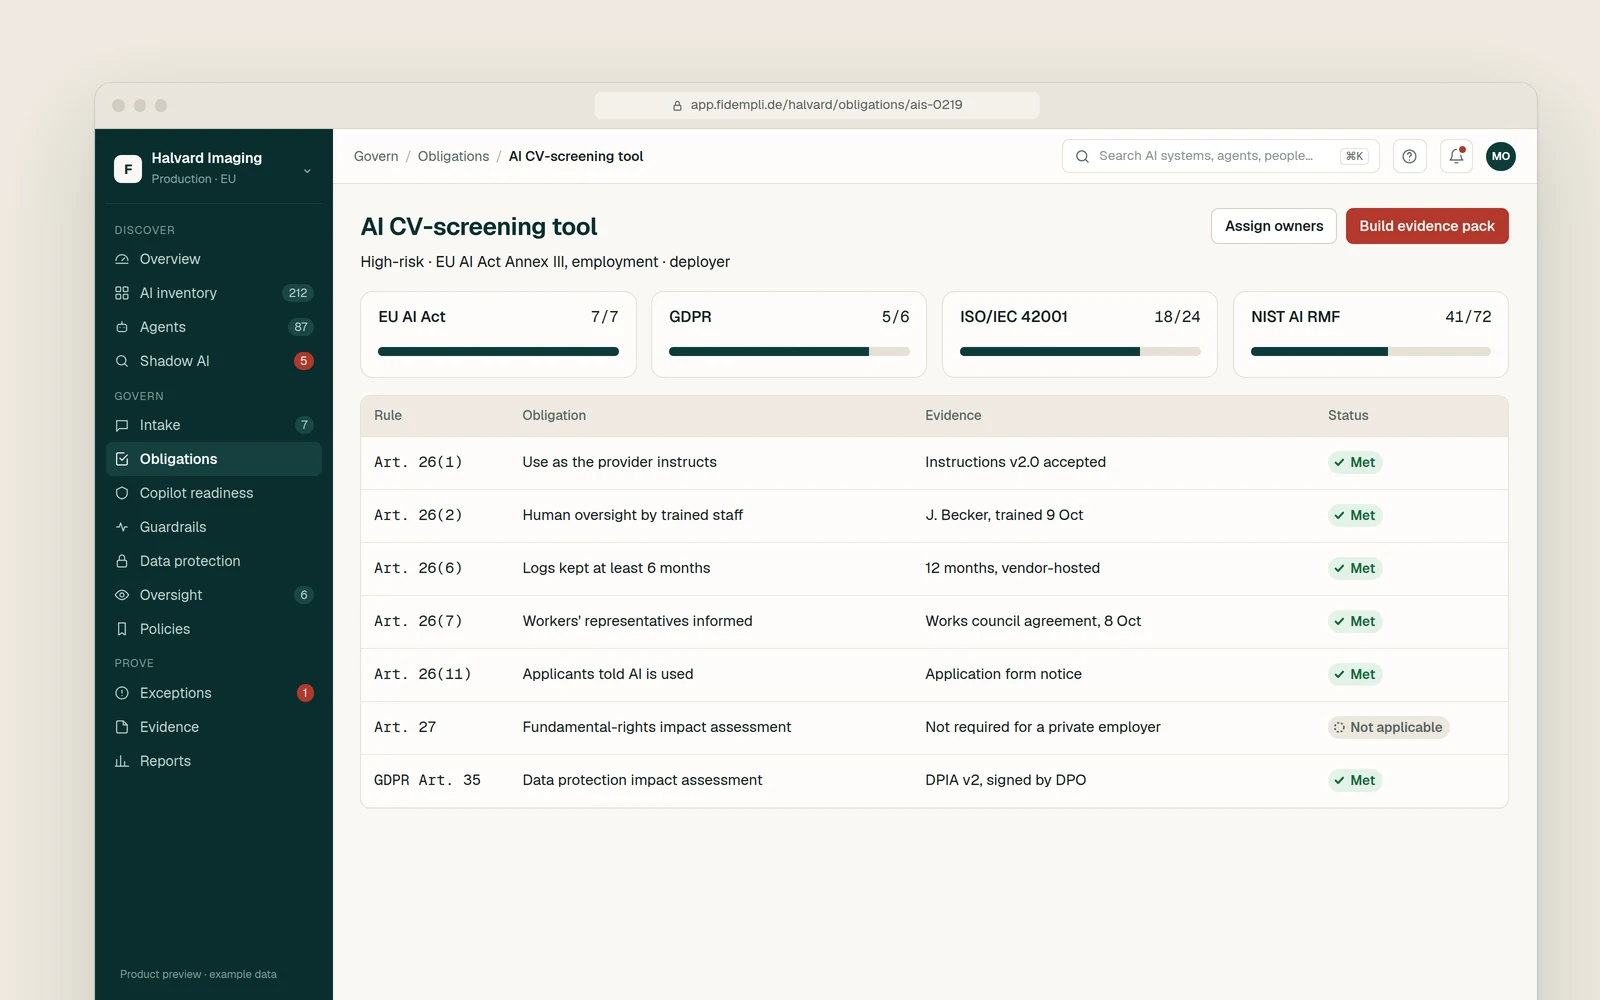
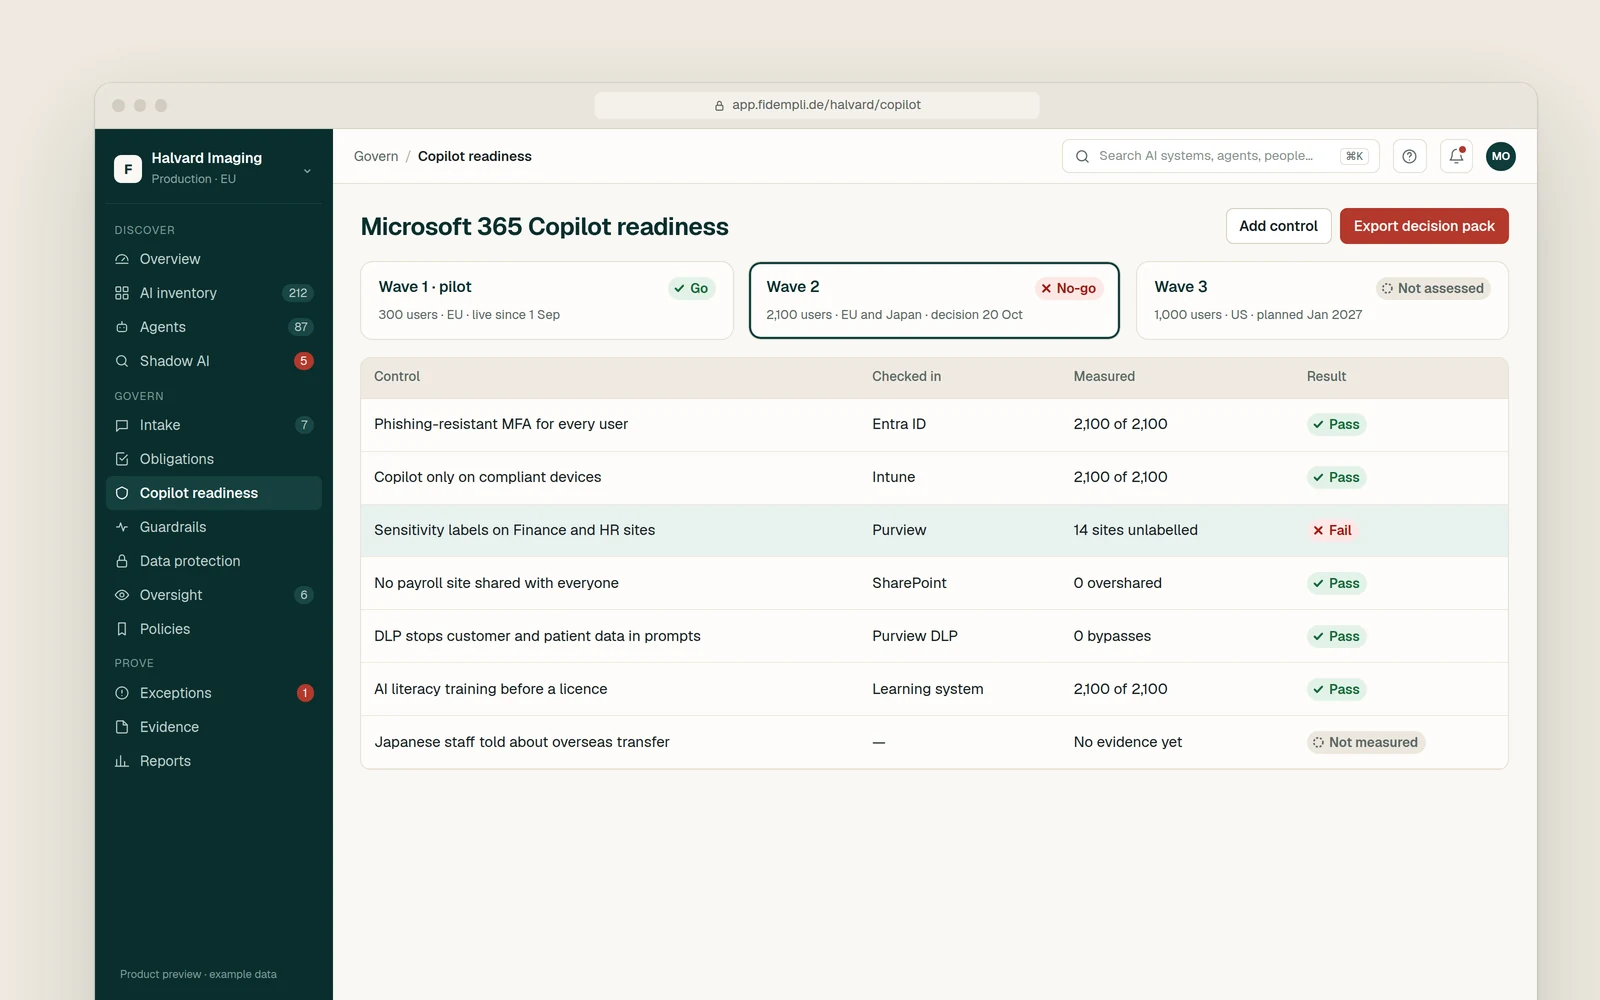
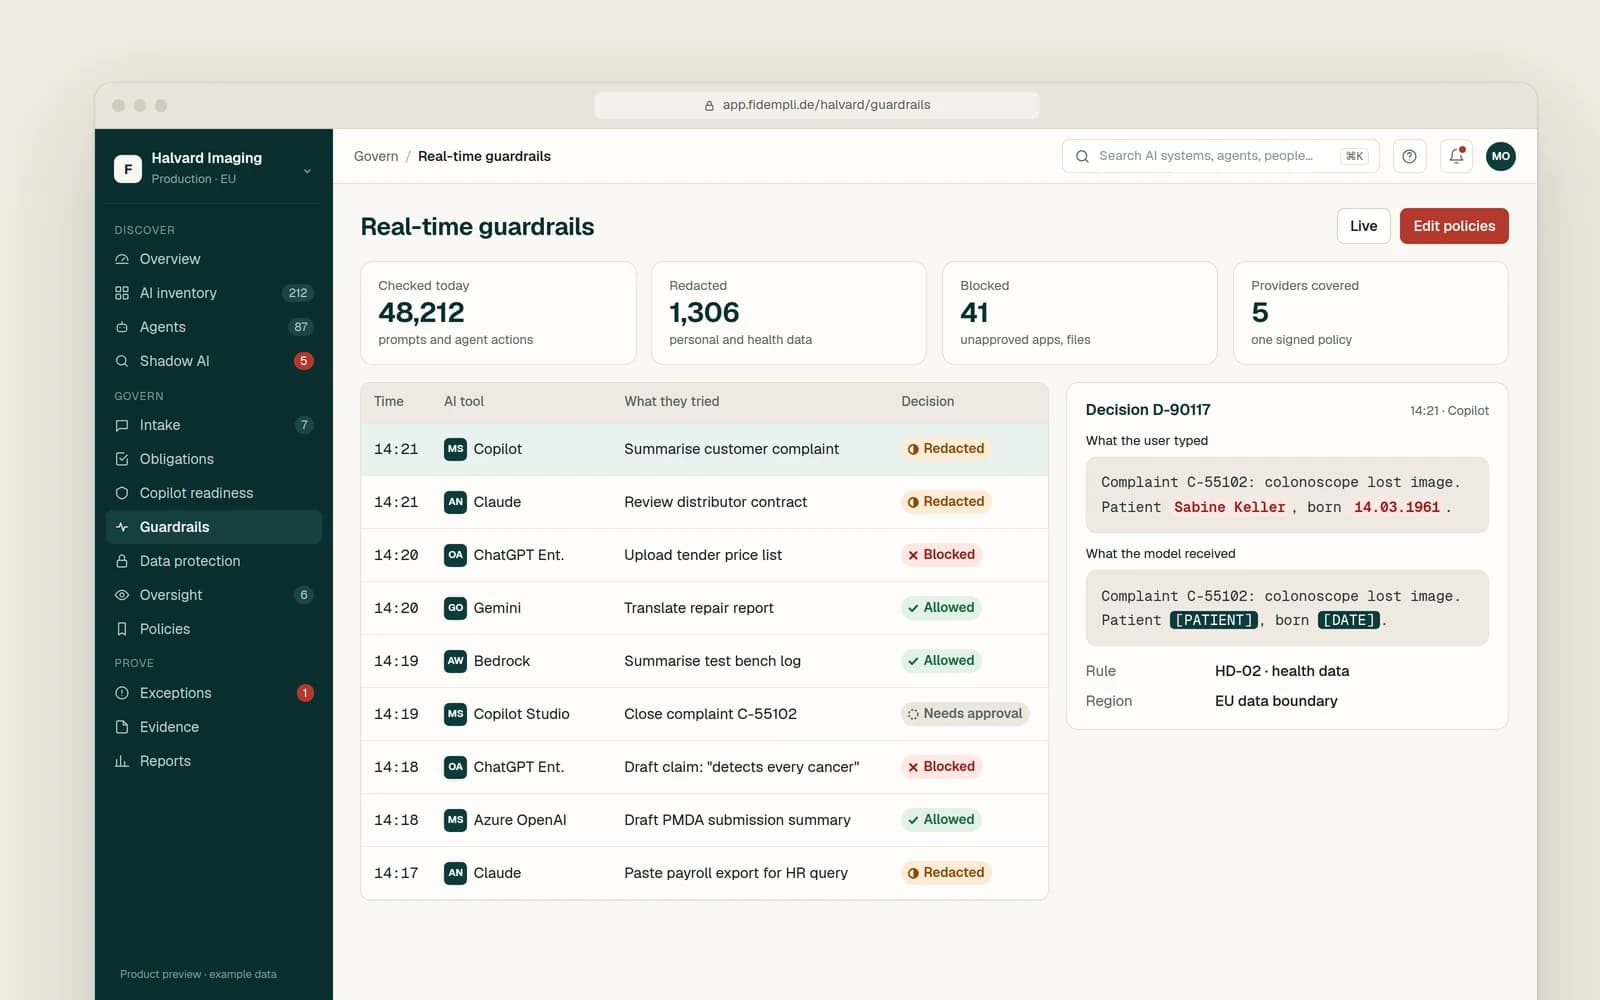
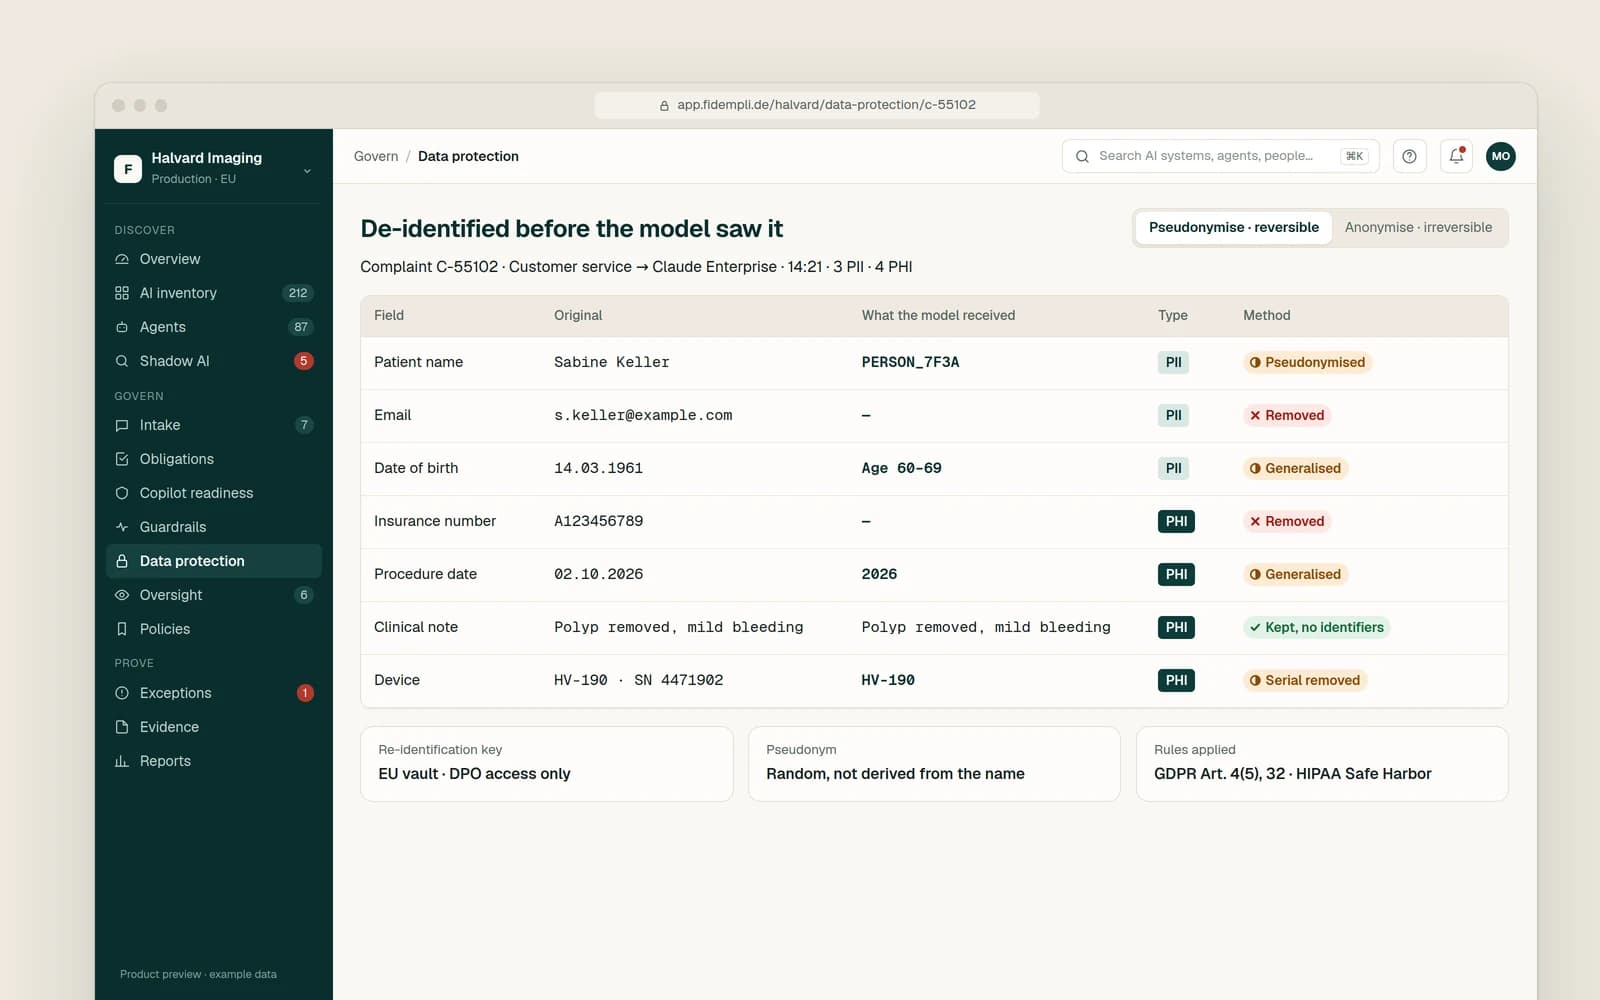
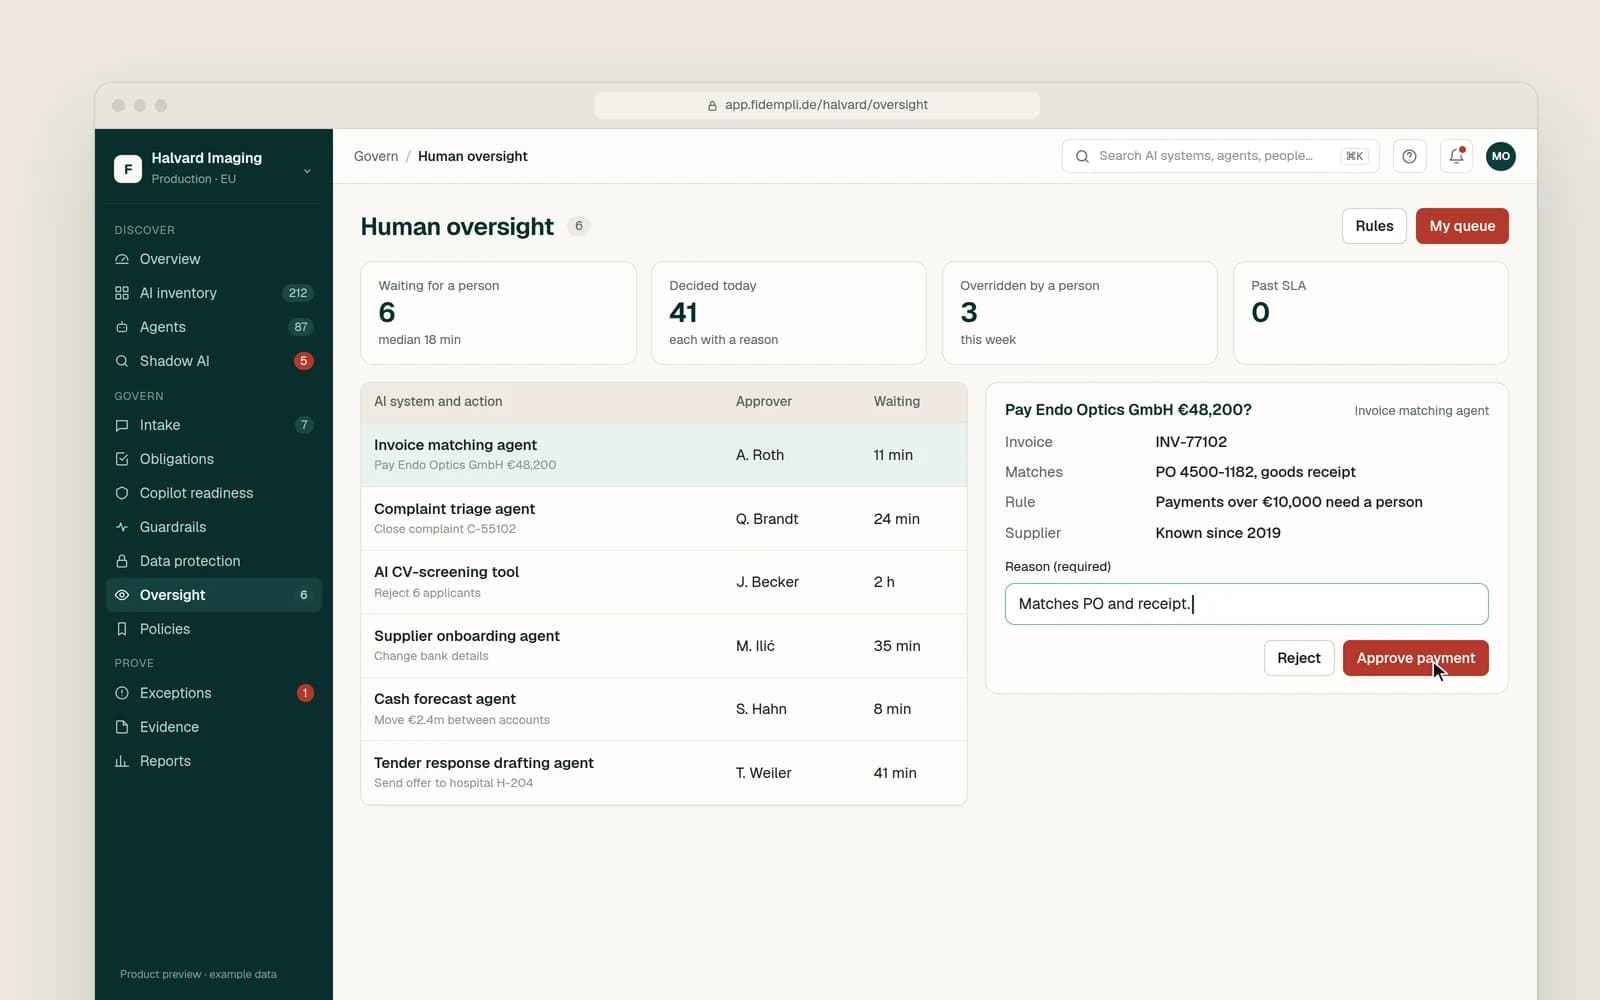
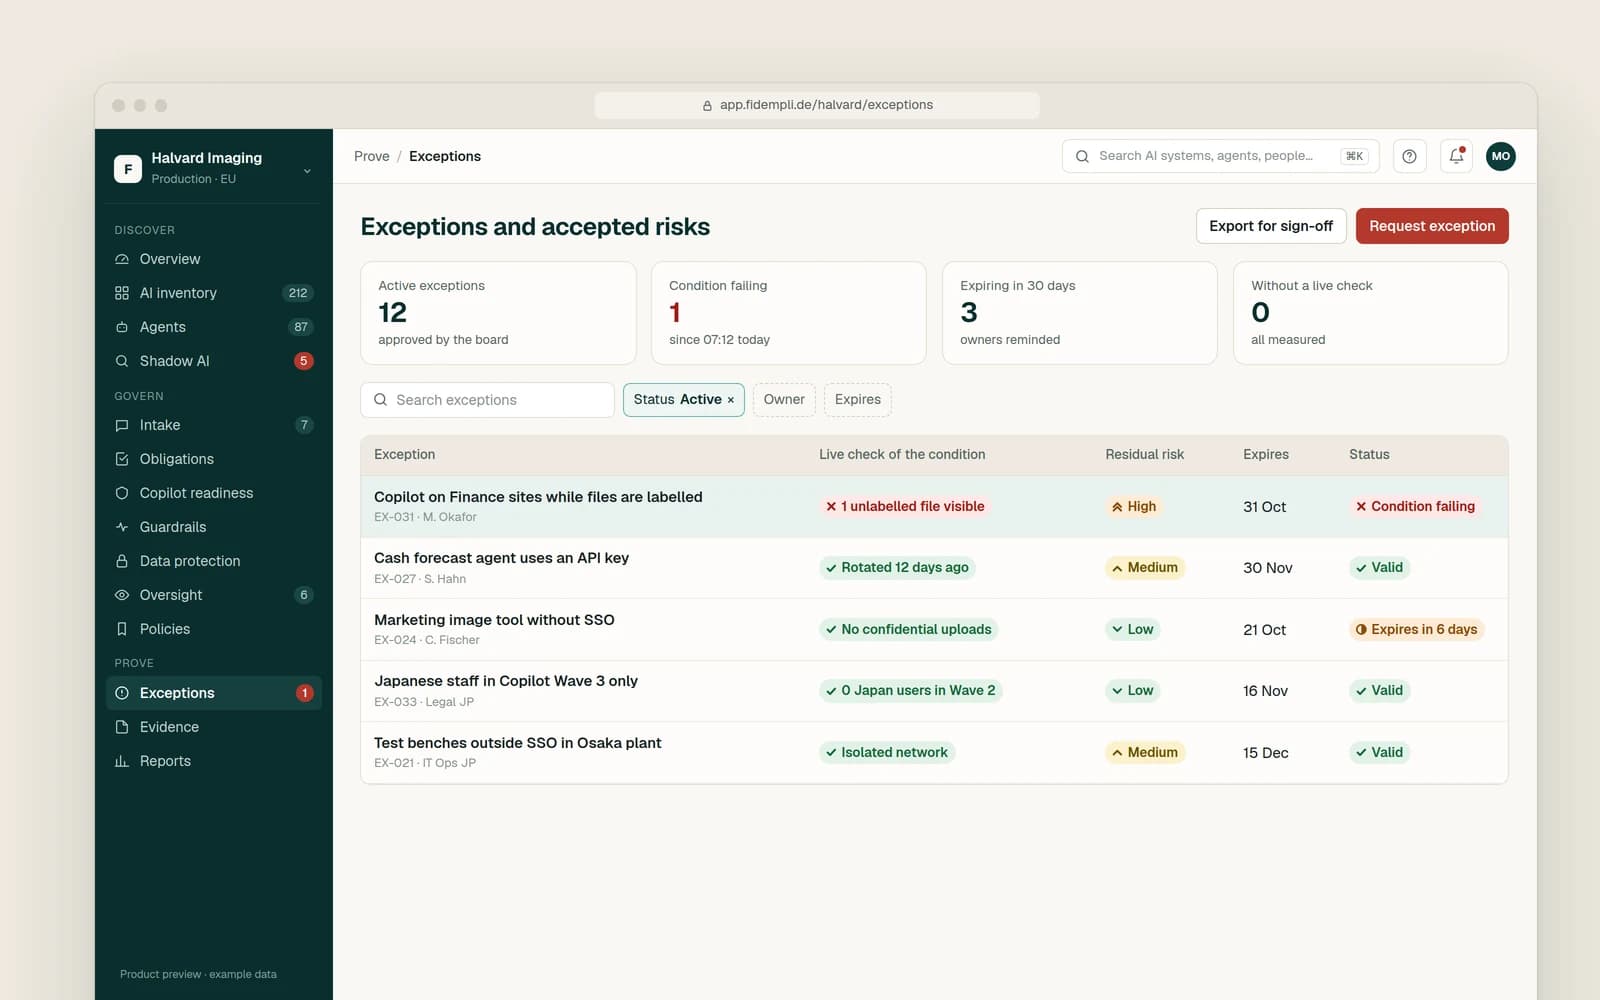
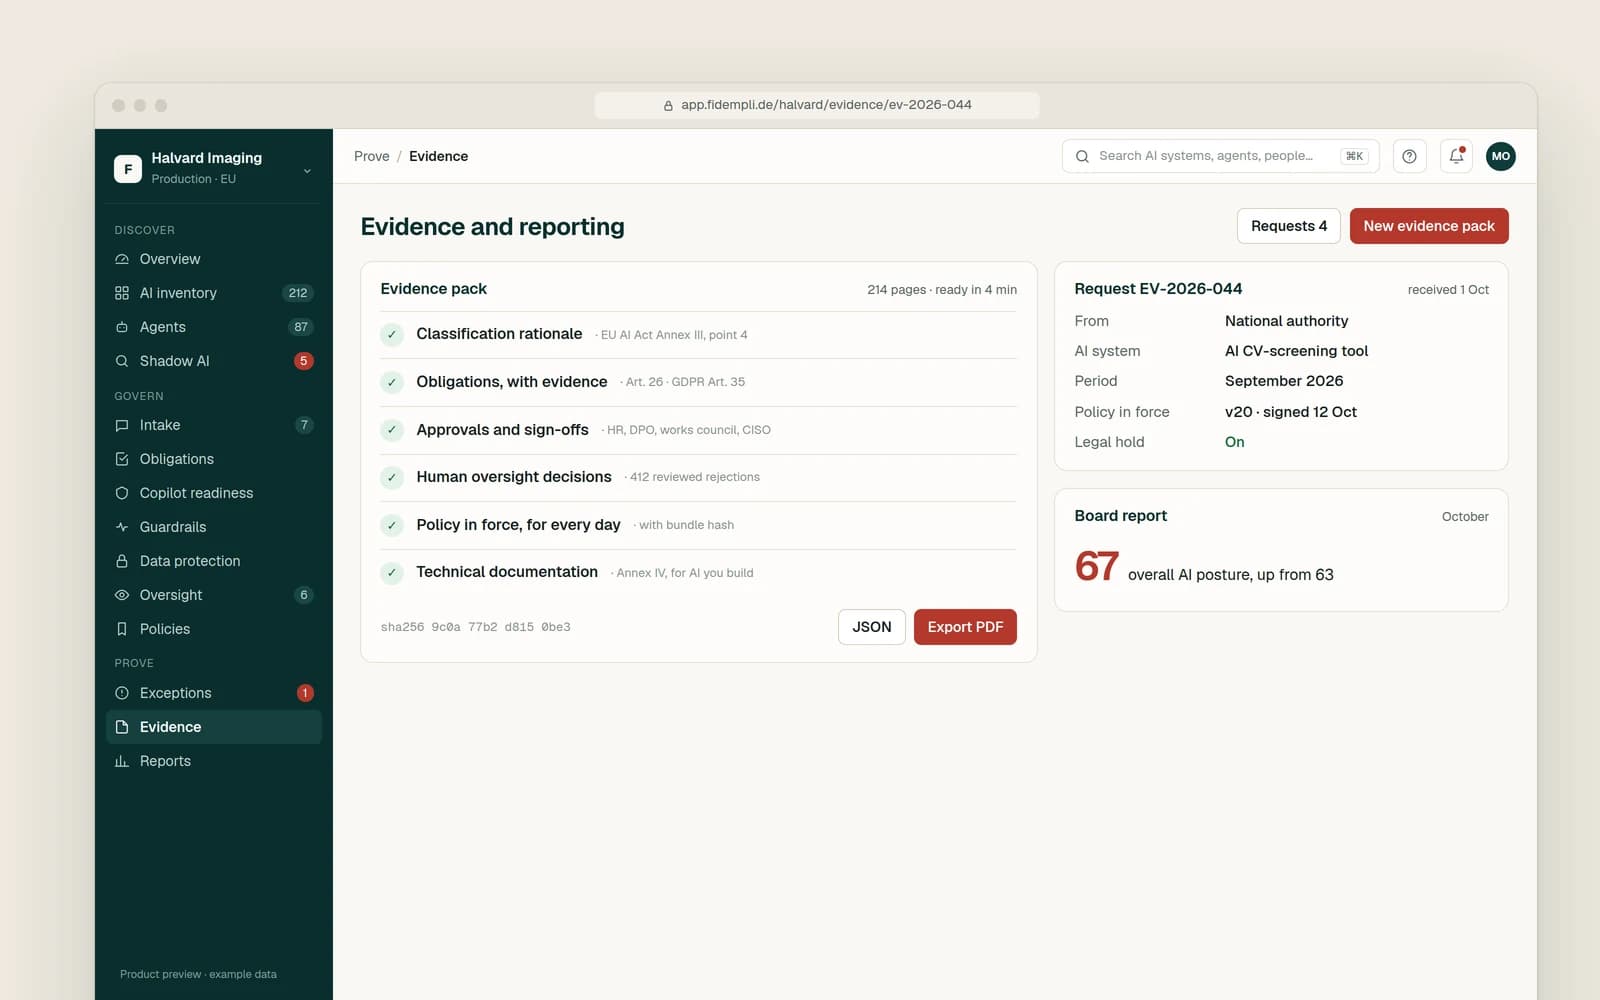
Product preview with example data
How Fidempli fits together
One platform. Two service pillars. Three ways to deliver.
The platform governs your AI. Our security and privacy experts assess, implement and run it with you – and AI automation does the repetitive work in every service.
Your requirements
EU AI ActGDPRNIS2DORAISO/IEC 42001 and 27001Data sovereignty- 01 DiscoverFind every AI system, agent and app in use, from every provider, including the ones nobody approved.
- 02 GovernRoute each new AI use by risk, map it to the rules that apply and check Copilot against your live tenant.
- 03 ProtectKeep personal, health and confidential data out of prompts, and put a person in front of high-stakes actions.
- 04 ProveTrack every accepted risk and answer auditors, authorities and the board with evidence, not self-assessment.
Service pillar 1
AI Governance, Privacy & AI Security
AI Readiness Assessment · EU AI Act Compliance · AI Privacy & Data Protection · AI Security & Red Teaming · AI Risk Management & ISO/IEC 42001 · Platform Implementation · Managed AI Governance
Service pillar 2
Cybersecurity & Privacy
Security Strategy & Architecture · Identity & Access Management · Cloud Security · GRC, ISO 27001, NIS2 & DORA · Healthcare & MedTech Security · Security & AI Training
Consulting
Assess, advise and design: readiness, strategy, roadmaps and architecture.
Professional services
Implement and integrate: we build and configure it in your environment.
Managed services
We run it for you, every day, with reporting you can show.
Data sovereignty
Your AI governance stays in your jurisdiction.
Run the platform where your regulator expects it, with control over your keys and your data location.
SaaS, EU region
Fastest start. EU-hosted in Frankfurt.
Private cloud
In your own cloud tenant.
On-premises
In your own data centre.
Air-gapped
No outbound connection at all.
Key control
Fidempli-managed keys At launchBring your own key At launchYour HSM At launchAI automation in every service
Automation does the repetitive work. Experts make the decisions.
AI systems, agents and shadow AI found from the platforms you already use.
Risk tier and obligations proposed for each system, reviewed by a person.
Identity, cloud and Copilot controls checked against live configuration data.
Decisions and policy versions collected for audits as they happen.
Services
Security and privacy experts who implement it with you.
AI Governance, Privacy & AI Security
- AI Readiness Assessment
- EU AI Act Compliance
- AI Privacy & Data Protection
- AI Security & Red Teaming
- AI Risk Management & ISO/IEC 42001
- Platform Implementation
- Managed AI Governance
- Consulting
- Professional services
- Managed services
Cybersecurity & Privacy
- Security Strategy & Architecture
- Identity & Access Management
- Cloud Security
- GRC, ISO 27001, NIS2 & DORA
- Healthcare & MedTech Security
- Security & AI Training
- Consulting
- Professional services
- Managed services
Start here
AI Readiness Assessment
In 3–5 weeks: an inventory of all your AI including shadow AI, EU AI Act classification per system, a privacy and security review, and a board-ready roadmap. The results move straight into the platform.
Price [Price]
Price [Price]
Price [Price]
Why Fidempli
Governance with a security backbone.
12+ years of identity, cloud and data protection work behind every AI control.
Personal data is removed or pseudonymised before any AI model sees it.
Policies act on every prompt and agent action, with evidence.
Built in Hamburg for the EU AI Act, GDPR, NIS2 and DORA.
Solutions
Built for the rules you answer to.
Each AI system is mapped to the obligations that apply to it, with the evidence attached. One set of evidence serves several frameworks.
EU AI Act
EU AI Act compliance, from inventory to evidence.
Learn moreGDPR and data protection
Use AI without losing control of personal data.
Learn moreISO/IEC 42001
Run an AI management system you can certify.
Learn moreNIST AI RMF
Govern, map, measure and manage AI risk.
Learn moreNIS2 and DORA
Bring AI into your NIS2 and DORA controls.
Learn moreMicrosoft 365 Copilot
Switch on Copilot with evidence, not hope.
Learn moreHealthcare and MedTech
AI governance for healthcare and medical technology.
Learn moreAll solutions
Each solution maps the requirements of a framework, product or industry to the platform capabilities and services that meet them.
Learn moreIndustries
For regulated European organisations.
- Financial servicesDORA · NIS2 · EU AI Act · GDPR · PCI DSS
- Healthcare & MedTechEU MDR/IVDR · EU AI Act · GDPR · NIS2
- Pharma & life sciencesGxP · EU GMP Annex 11 · GDPR
- Manufacturing & automotiveNIS2 · Cyber Resilience Act · TISAX · ISO 27001
- Energy & utilitiesNIS2 · KRITIS · OT security
- Retail & e-commerceGDPR · PCI DSS · EU AI Act
- Technology & SaaSEU AI Act · GDPR · Cyber Resilience Act · ISO 27001
- Public sectorEU AI Act · NIS2 · GDPR · BSI IT-Grundschutz
Start with a 30-minute AI risk conversation.
A senior consultant replies within one business day. Or join the 3–5 design partners shaping the platform before launch.